Reason
Required, in words, for every exemption.
CONSTELLATION PRODUCT / COMPLIANCE & GOVERNANCE
Constellation checks live cluster objects on a schedule, maps each check to the frameworks it supports, and records every exemption and change in an audit log you can verify. Access is role-based, with single sign-on and expiring tokens.
Alpha · Mapping is not certification · Some runners optional01 / EVIDENCE
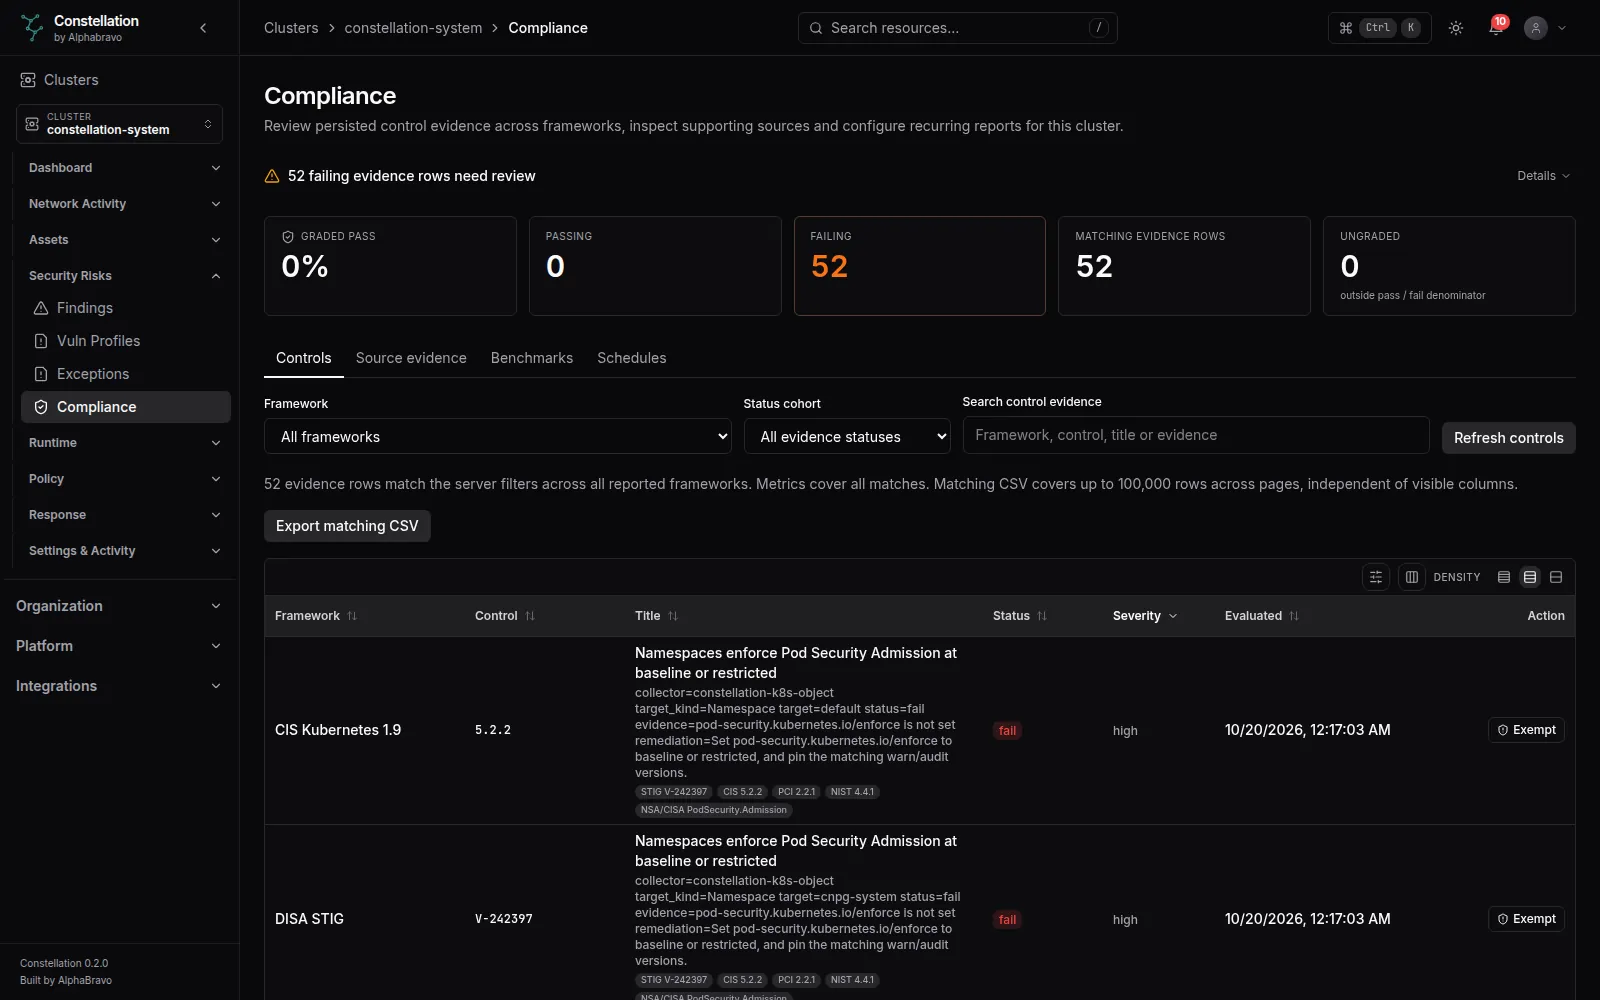
A compliance collector runs every 6 hours by default and evaluates live objects: Pod Security labels on namespaces, wildcard RBAC roles, host networking, privileged containers and read-only root filesystems. Add your own checks in CEL.
02 / FRAMEWORKS
Each check is mapped to the framework controls it supports, so one result counts wherever it applies. The catalog includes CIS Kubernetes, CIS Docker, the NSA/CISA Kubernetes Hardening Guide, NIST SP 800-53 and SP 800-190, PCI DSS 4.0 and others. Define custom frameworks for your own control set.
A mapped check is evidence for a control, gathered when it ran. It does not certify a cluster or attest compliance with any framework. Coverage differs a lot by framework and is thin for many; review the mapping with your assessor.
You can define compliance schedules and report formats in the console and API, but the scheduler that runs and delivers them is not part of any shipped deployment in this alpha.
03 / EXEMPTIONS
Exempting a control requires a reason and an expiry. The approving user is recorded, an exemption can be revoked, and creating or revoking one writes an audit event. Exempted checks show as exempted, not passed.
Vulnerability exceptions follow the same pattern: a reason, an expiry of at most 30 days and an audit record. See vulnerabilities.
Required, in words, for every exemption.
Required. An exemption cannot be open-ended.
Who approved it, when, and when it was revoked, in the audit log.
04 / AUDIT LOG
Each audit event is chained to the one before it with SHA-256, and the database refuses updates and deletes on the audit table. Verification walks the whole chain and reports the first break.
An optional archiver exports each day’s events to S3-compatible storage with a manifest of hashes and row count, signed with an Ed25519 key or keyless with cosign. It verifies the chain first and refuses to archive a broken one.
The archiver is off by default. Verification runs from the API or the CLI; the console’s audit page has no verify button yet.
constellationctl audit verify
constellationctl audit compliance-export --framework <id> --control <id>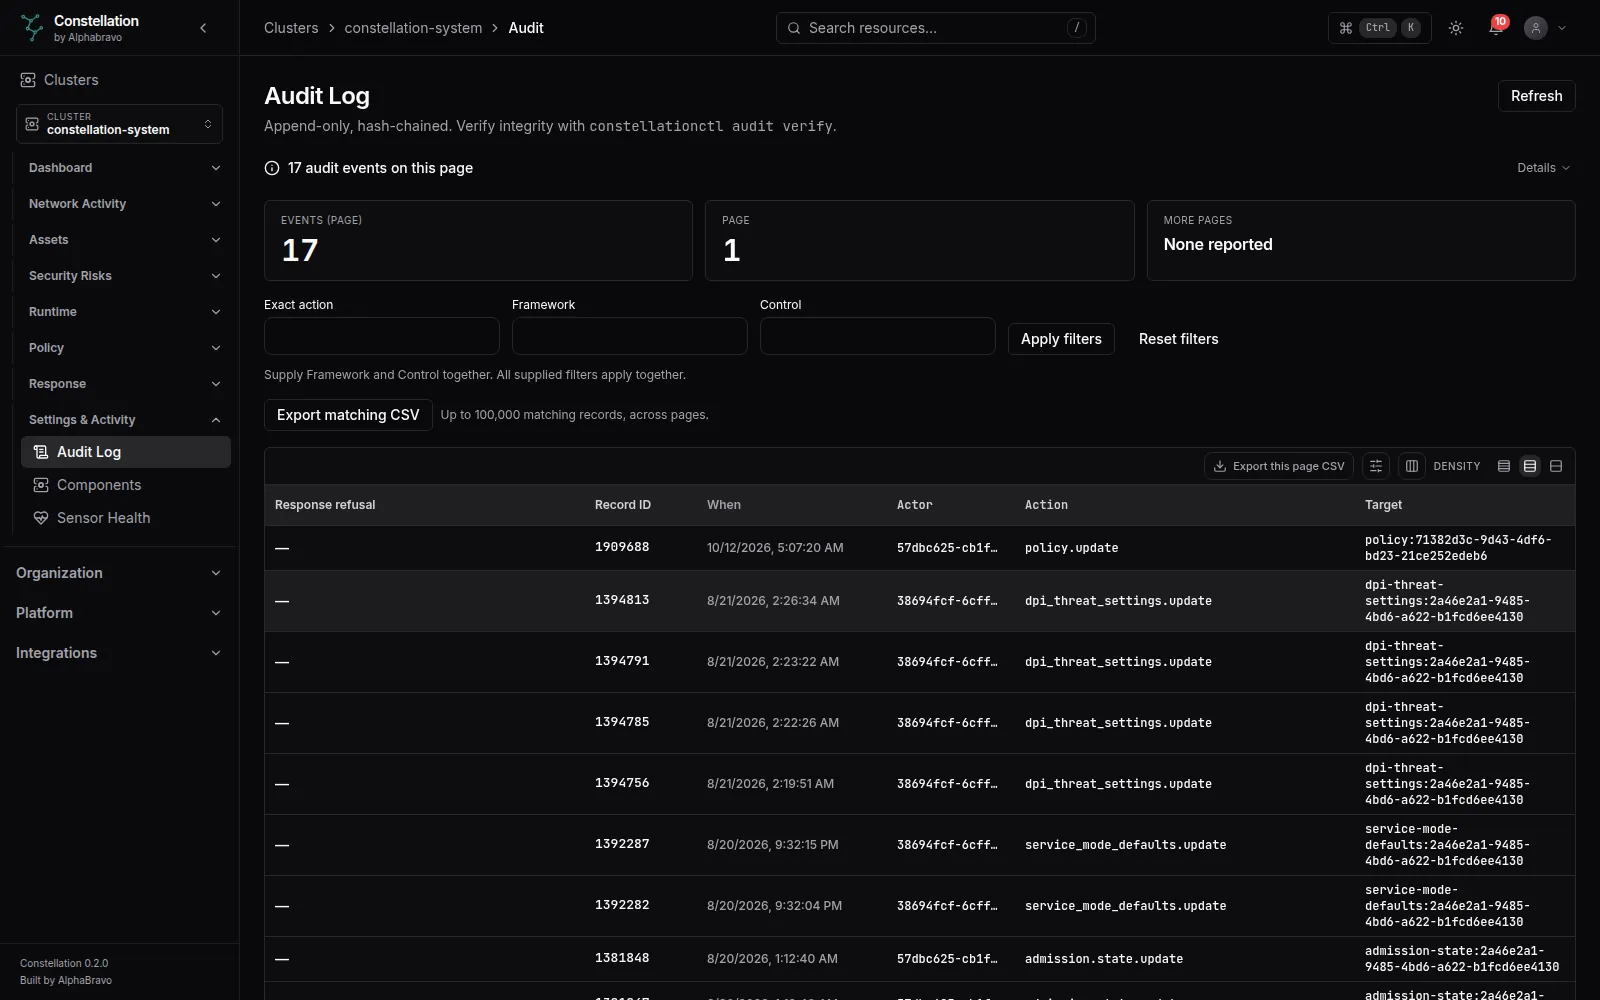
05 / ACCESS
Five built-in roles (GlobalAdmin, SecurityAdmin, ClusterAdmin, Analyst and Auditor), custom roles and scoped role bindings that can expire.
Local accounts with password, history, age, session and lockout policy. OIDC, SAML 2.0 and LDAP/Active Directory, with group-to-role mapping and optional just-in-time users.
Scoped tokens with a required expiry, stored hashed, that can be rotated and revoked from the API or CLI. Service accounts for automation.
Scanners, runtime agents and federation peers get token-only permissions that cannot be granted to people.
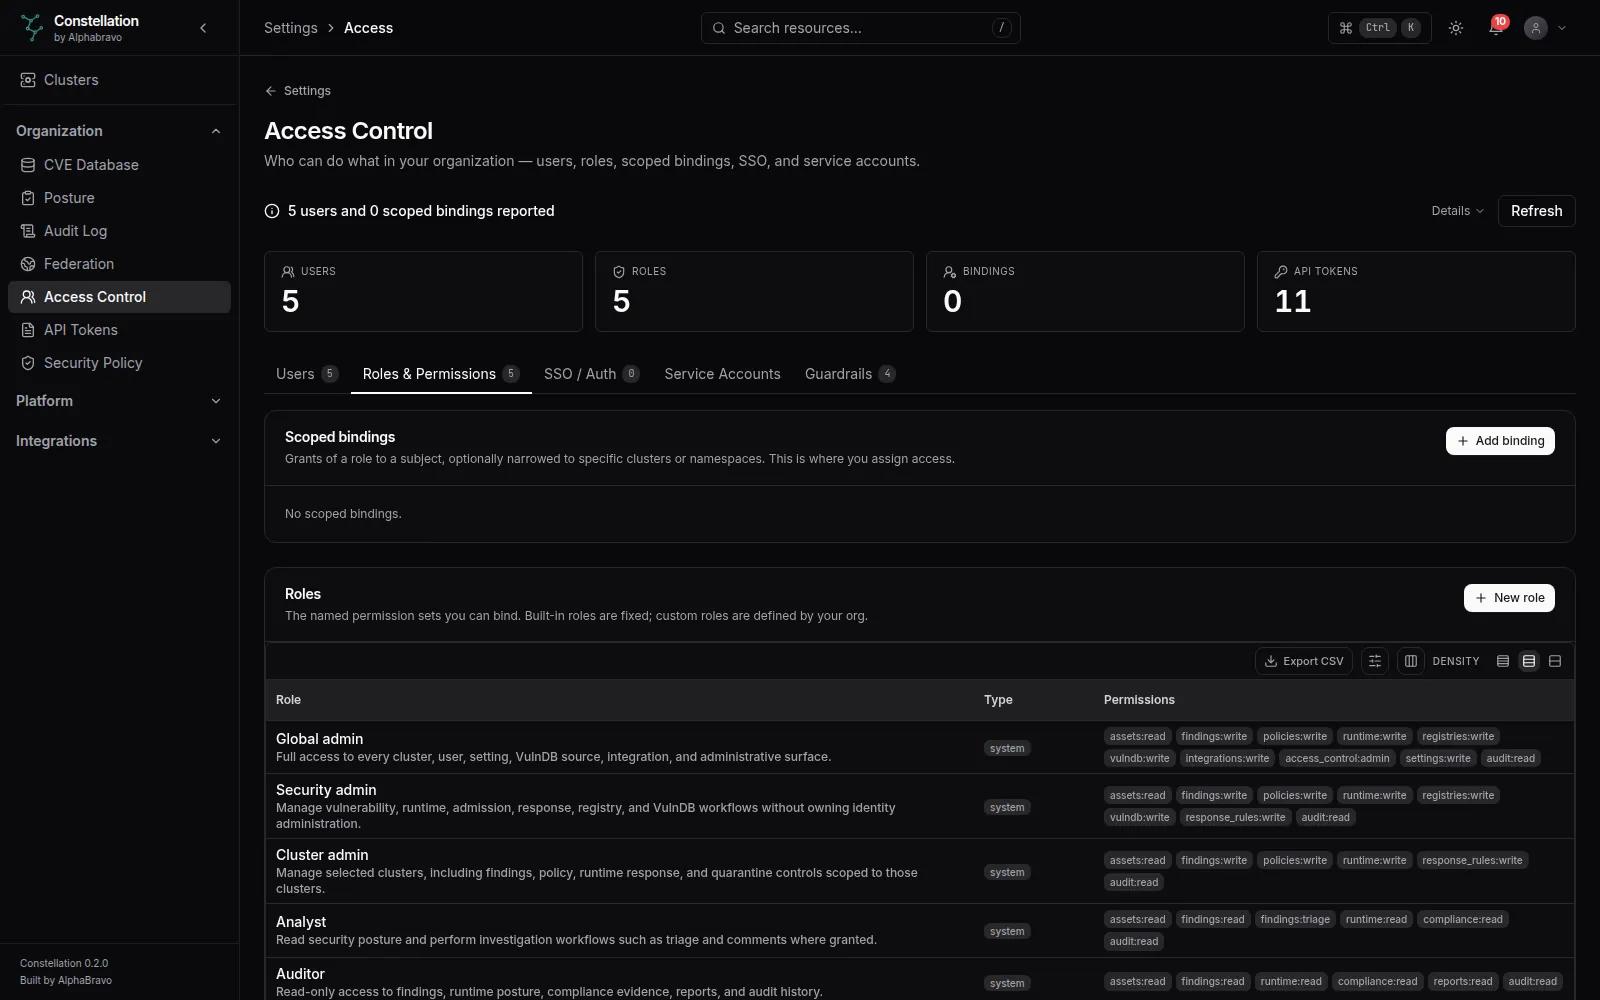
There is no built-in multi-factor authentication; require it at your identity provider. Deployments run one organization today.
06 / OPERATIONS
Webhook, Slack, Microsoft Teams, PagerDuty, Jira, ServiceNow and email. Payloads are HMAC-signed; every delivery is recorded and retried with backoff. Syslog forwarding in RFC 5424, JSON or CEF over UDP, TCP or TLS.
Per-organization backups to local disk or S3, signed with an Ed25519 key or keyless, on a schedule with retention. Restore verifies the signature first.
Build versions, restarts, version drift and stale or crashlooping components for the control plane and each cluster, and a redacted support bundle.
ArchitectureFAQ
No tool can. Constellation gathers evidence and maps it to controls. It does not certify a cluster or attest compliance, and its mappings cover some controls of each framework, not all of them. #
They can run chain verification through the API or CLI, and with the archiver on, check the signed daily manifests in your storage. #
The console produces compliance and executive reports. PDF rendering needs a tool that the API image does not include, so today you print them to PDF from the browser. #
NEXT STEP
Tell AlphaBravo which framework your assessors use. We will show which checks map to it and where the gaps are.