Narrow it down
Filter by time window, verdict, namespace and group, and save the views you come back to.
CONSTELLATION PRODUCT / NETWORK
Constellation records which workloads talk to which, turns those observed flows into candidate network policies, and rolls them out only after someone approves them. Every step is audited and can be undone.
Alpha · Visibility on by default · Nothing enforced until applied01 / TRAFFIC MAP
The runtime agent’s data plane reports connections between pods: bytes, packets, sessions, the application protocol detected and the policy verdict. The network workspace shows them as a map, folded conversations, live sessions, packet captures, rules and DPI threats.
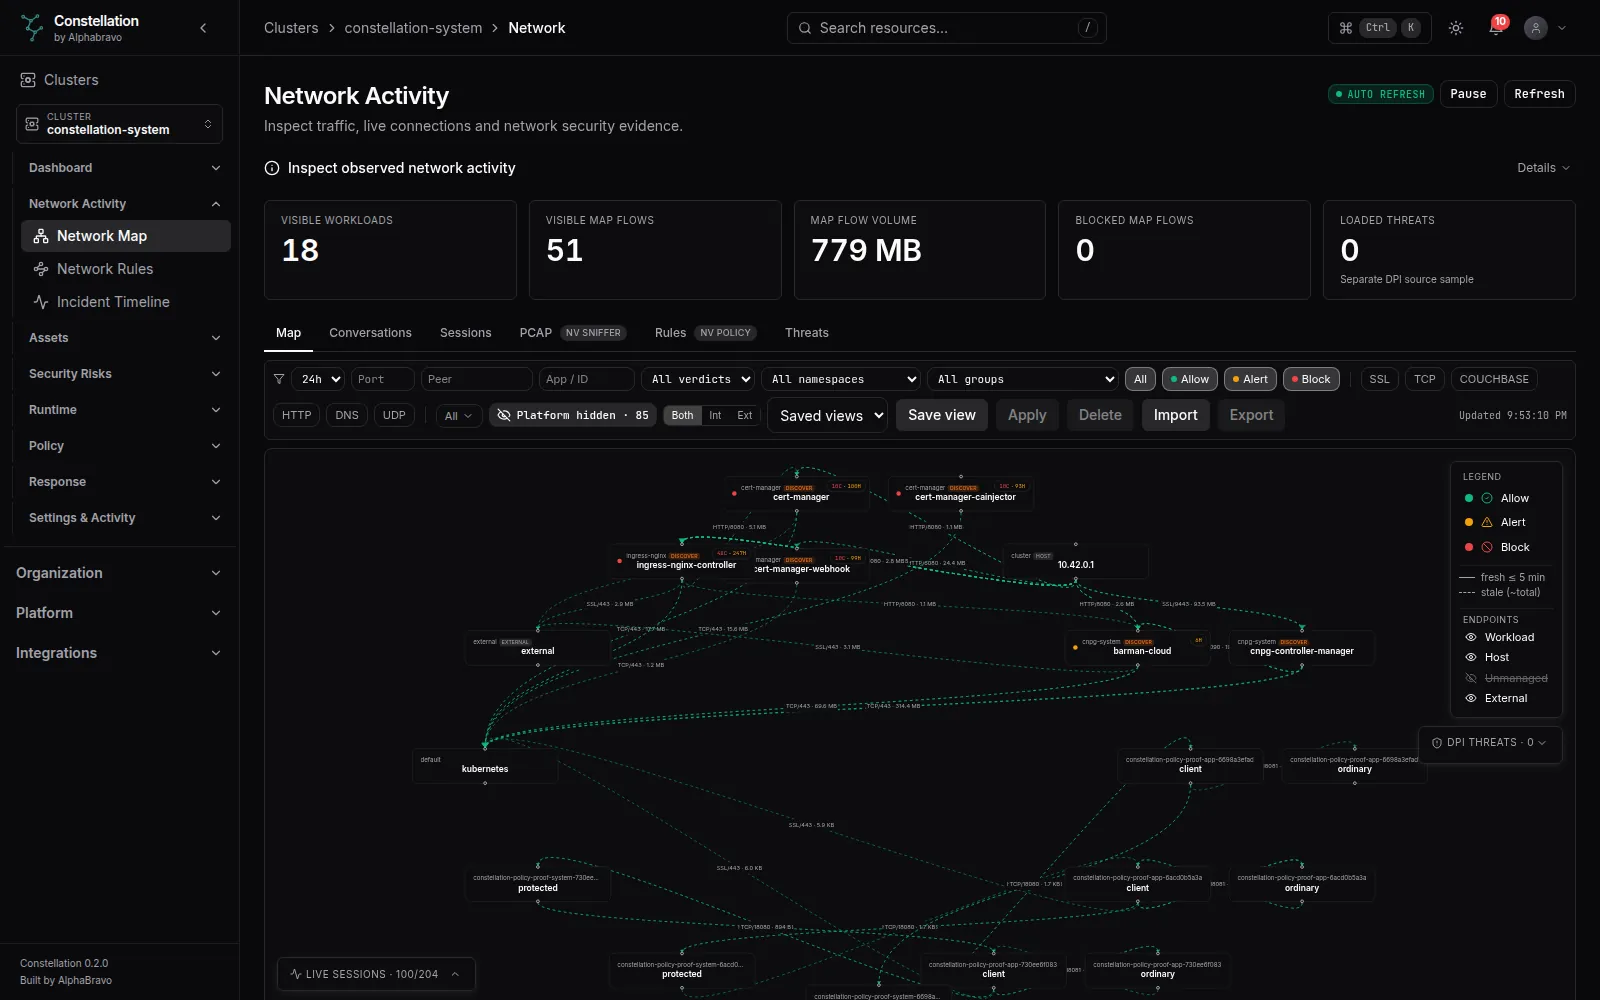
Filter by time window, verdict, namespace and group, and save the views you come back to.
Workloads that talk to the outside world, alongside their vulnerabilities, so exposure and CVEs are read together.
Isolate a workload with a default-deny NetworkPolicy, or kill a live session, from the map.
02 / POLICY LIFECYCLE
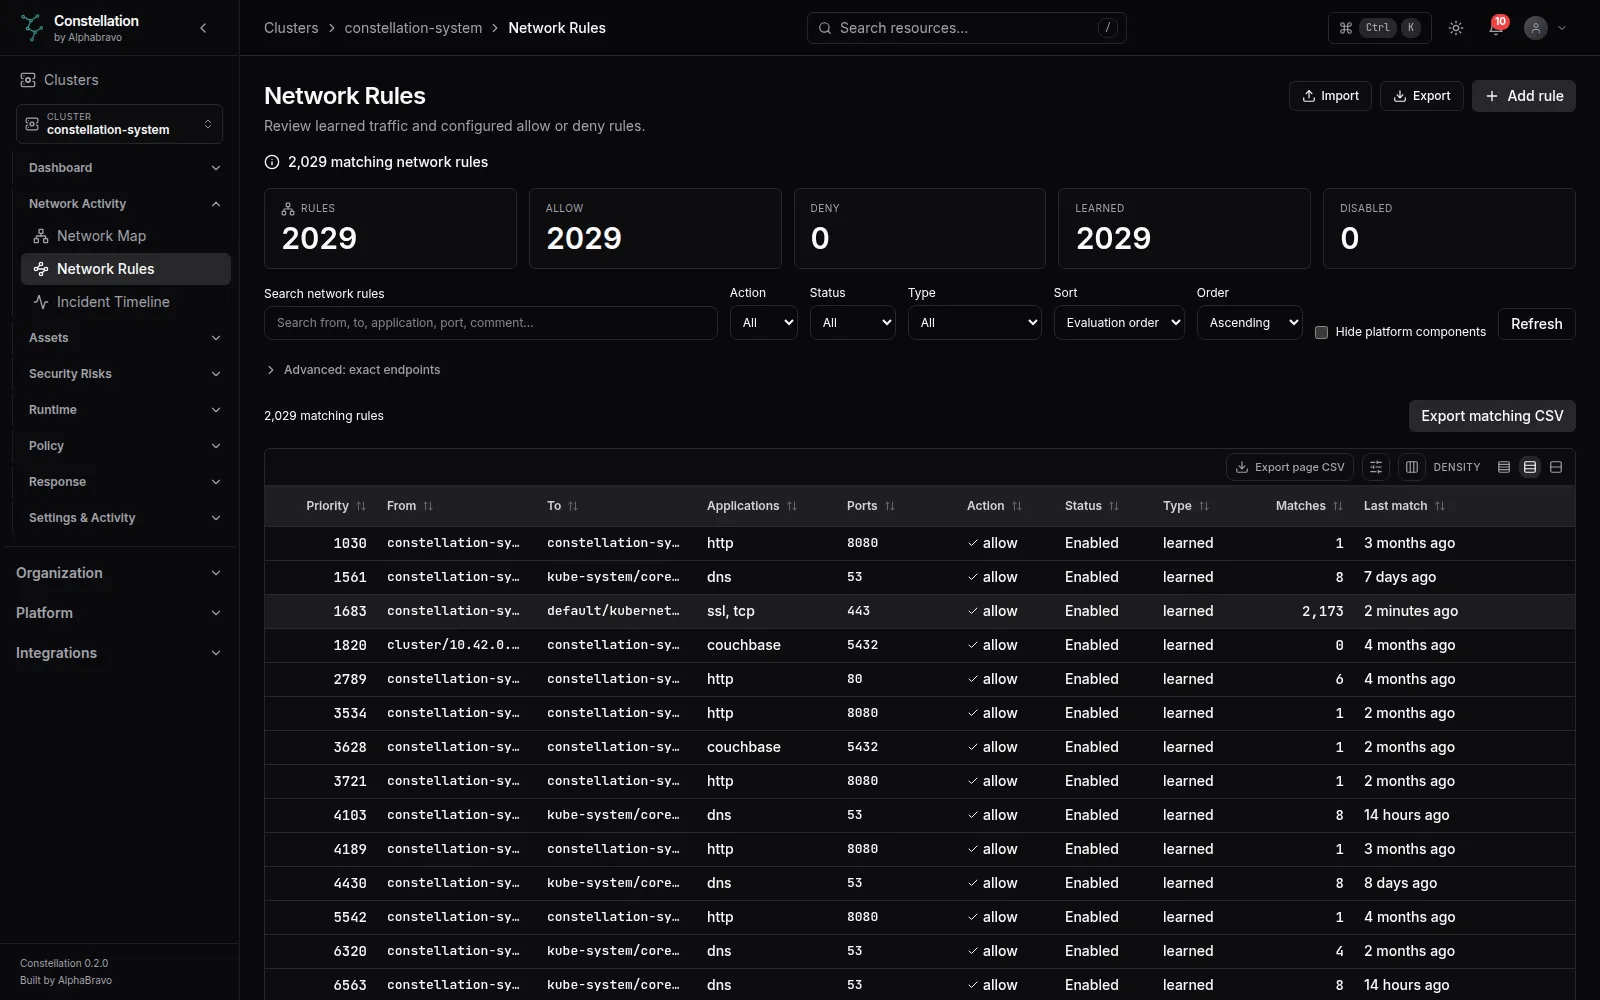
Constellation generates a candidate policy per workload from the flows it saw. A person approves it; applying it requires that approval and an unchanged candidate, so a policy that changed after review must be reviewed again. Workloads move from Discover to Monitor to Protect.
Nothing is enforced until an operator approves and applies a policy. Constellation’s own component NetworkPolicies are a separate chart setting, off by default.
03 / CNIs
Policies render as native Kubernetes NetworkPolicy, CiliumNetworkPolicy or Calico GlobalNetworkPolicy; choose one flavor per cluster. The CNI’s own enforcement is the primary path.
| CNI | Status | Notes |
|---|---|---|
| flannel, kindnet | Tested live on kind/k3s | Do not enforce NetworkPolicy themselves, so isolation by policy has no effect |
| Calico | Tested live on kind/k3s | Native or Calico policy flavor |
| Cilium | Tested live on kind/k3s | Native or Cilium policy flavor; the agent’s inline data plane does not enforce in eBPF mode |
| EKS, GKE, AKS CNIs | Unit-tested only | Not yet run live |
| GKE Autopilot | Not supported | Privileged DaemonSets are not allowed |
FAQ
No. The policy applier is installed, but it only applies policies an operator has approved and moved to Protect. #
The agent can read flows from a Hubble relay on Cilium clusters, but connecting it is a manual agent setting today, not a chart value. Plan for it in an evaluation. #
A block-IP action exists for Cilium clusters. Native NetworkPolicy is allow-list only, so it cannot express it. #
NEXT STEP
Tell AlphaBravo which CNI you run. We will walk through generating and approving a first policy.